


 Compliance-first delivery
The problem
Cost and security tooling is either cloud-specific or priced for large enterprises. Smaller teams on two or three clouds checked each console by hand, found idle resources months late and learned about an open storage bucket from someone else.
What we built
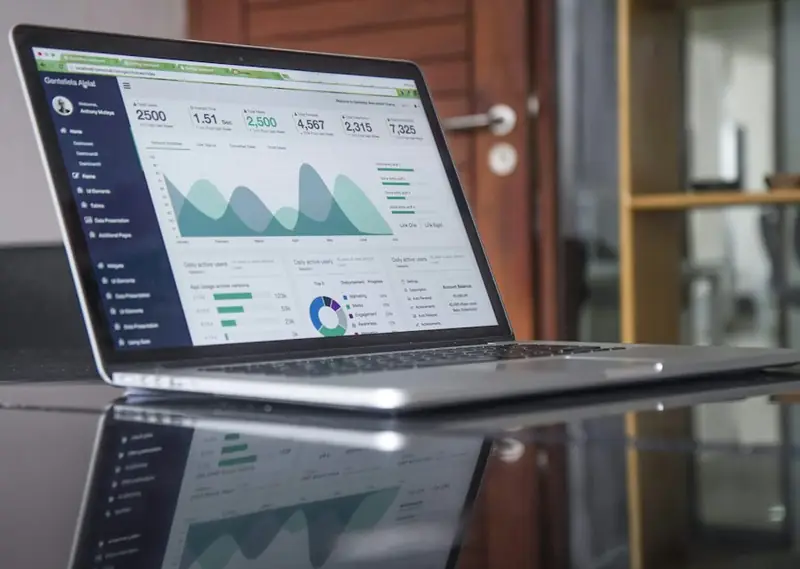
A multi-tenant Laravel application that connects to each cloud with read-only credentials, inventories resources, runs security checks, recommends cost fixes and flags unusual daily spend.
Where it stands
Live at cloud-monitor.radiatus.com with a free tier. We use it ourselves and in client cost reviews to see where a bill is going before changing anything.
Numbers you can check
Every figure on this page comes from the running product or its source code, checked on 7 November 2026. None is a client result.
| Figure | What it counts | Where it comes from |
|---|---|---|
| 3 | Cloud providers behind one provider contract: AWS, Azure, Google Cloud | The application's provider implementations |
| 17 | Security checks: 9 on AWS (S3, EC2, security groups, RDS, IAM), 4 on Azure, 4 on Google Cloud | The compliance engines per provider |
| 13 | AWS resource types inventoried, from EC2, EBS and RDS to Lambda, DynamoDB, load balancers, Route 53 and VPCs | One reader per resource type |
| 28 days | Trailing baseline each day's spend is scored against (z-score, default threshold 2.0) | The anomaly detector |
| 3 | Alert types sent by email: monthly budget, new critical finding, stale access key | The alert rule model |
| A–F | Security grade: 100 minus severity-weighted penalties | The scoring service |
Read-only, on purpose
The first design decision was the one that makes a monitoring tool safe to connect: CloudMonitor never needs permission to change anything. On AWS it uses read-only roles and calls APIs such as Cost Explorer, CloudWatch metrics and CloudTrail lookups. On Azure it authenticates with client credentials against Azure Resource Manager and queries Cost Management. On Google Cloud it signs its own short-lived tokens. A leaked CloudMonitor credential can read an inventory; it cannot delete a database or open a port.
One contract, three clouds
Each cloud sits behind the same provider contract: list resources, fetch costs, run checks. AWS uses its official PHP SDK. Azure and Google Cloud are called over their REST APIs directly, which kept dependencies small and made the code that handles authentication easy to audit. Adding a fourth provider means implementing the contract, not touching the dashboard.
Scheduled jobs sync inventories, evaluate alert rules hourly and build daily reports. Every record is scoped to a tenant, so data from different organisations never mixes, and one organisation can connect several cloud accounts.
Spend anomalies without false alarms
Simple "spend went up 20%" rules fire every month-end and every launch. CloudMonitor scores each day's spend against a trailing 28-day baseline using a z-score, and ignores jumps smaller than one dollar so tiny accounts do not flap. Days already flagged are kept out of later baselines, so a single spike cannot raise the bar and hide the next one. The result is shown on the dashboard next to the services that drove it.
Security checks people act on
The 17 checks focus on the findings that cause real incidents: public storage, open security groups, unencrypted databases and disks, and stale or over-privileged IAM keys. Each finding has a severity, and the account grade is 100 minus severity-weighted penalties, from A to F. The checks are modelled on CIS-style controls; the product does not claim a formal CIS Benchmark mapping.
The stack
| Layer | Choice | Why |
|---|---|---|
| Application | Laravel 13 on PHP 8.3 | A mature framework with queues, scheduling and policies built in |
| AWS | AWS SDK for PHP: Cost Explorer, CloudWatch, CloudTrail and resource APIs | Official SDK with read-only roles |
| Azure and Google Cloud | REST APIs with client-credentials and signed-JWT authentication | Few dependencies, auditable auth code |
| Access control | Sanctum, role and permission package, activity log | Who saw and changed what, per tenant |
| Front end | Vite and Tailwind CSS | Fast dashboards without a separate SPA |
What it does not do yet
- Google Cloud spend is not shown yet: it needs a BigQuery billing export, which the product does not read today. Google Cloud inventory and checks work.
- Spend anomalies appear on the dashboard; they are not sent as email alerts. Email alerts cover budgets, new critical findings and stale keys.
- Checks are CIS-style, not a certified CIS Benchmark assessment.
What this means for your cloud bill
Most cloud cost work starts with the same three questions CloudMonitor answers: what is running, what is it costing, and what is exposed. In a cloud infrastructure or cost engagement we answer them for your accounts first, then fix the waste and the risky findings as code. Ongoing operations, including monthly cost reviews, are part of our managed services.
Our FinOps playbook explains the method behind the cost recommendations.
Questions about this case study
AWS, Microsoft Azure and Google Cloud. Inventory and security checks work on all three; spend reporting works on AWS and Azure, and Google Cloud spend needs a BigQuery billing export that is not supported yet.
No. It uses read-only credentials on every provider, so it can list resources and costs but cannot change or delete anything.
Each day's spend is scored against a trailing 28-day baseline using a z-score, small absolute jumps are ignored, and flagged days are kept out of later baselines. Anomalies are shown on the dashboard.
Seventeen: nine on AWS covering storage, compute, security groups, databases and IAM, four on Azure and four on Google Cloud. Findings roll up into an A to F grade.
Yes. We often start a cost or security review by connecting CloudMonitor read-only, then turn the findings into a prioritised fix list and make the changes as infrastructure code.
Need something like this for your organisation?
Tell us what you are connecting, running or securing. The engineers behind this case study reply personally.
- A senior engineer reads every enquiry
- Happy to sign an NDA first
- You get a written next step, not a sales sequence